
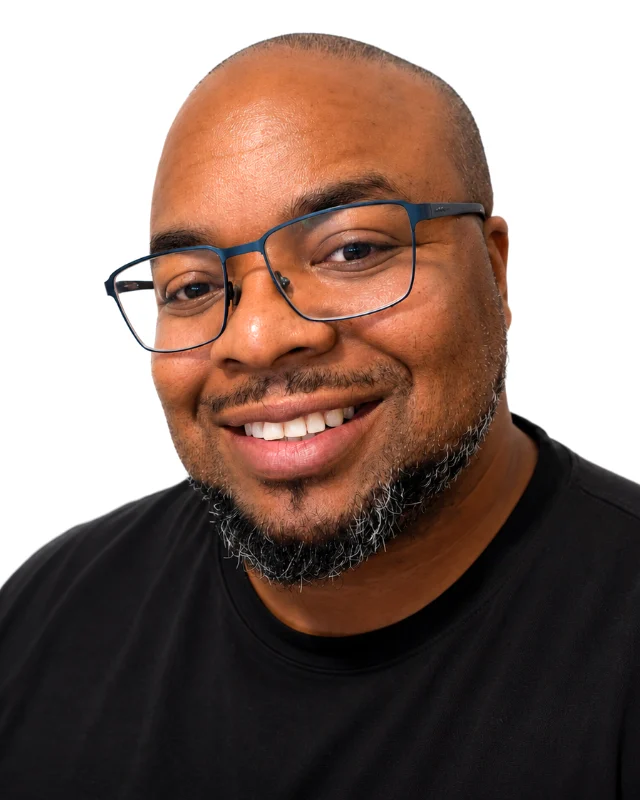
Author
Derrick Smith
Founder & CEO, MindVault. Named inventor on the patents behind it, and the author of every article on this site.
- Articles
- 19 articles
- Role
- Founder & CEO · MindVault
- Credentials
- 2 U.S. provisional patents · Wireless and embedded platforms
About
Derrick Smith is the founder and CEO of MindVault and the named inventor on both U.S. provisional patent applications behind it, covering behavioral pattern analysis and synthetic profile generation. He filed the IP before recruiting anyone, then brought in enterprise veterans ahead of production development.
His background is in wireless and embedded platforms, which is where the instinct behind MindVault comes from: systems that have to keep proving a link is still the link it was, long after it was first established. The research on this site is his argument, written for the people who have to defend the span after login.
Writes about
- Enterprise Positioning
- SOC Operations
- Threat Analysis
- Privacy by Architecture
- Category Strategy
- Post-Login Security
- Session Security
- AI Threats
- AI Security
- Threat Landscape
Derrick Smith leads the team on the Our Team page. Press and speaking enquiries go through the contact form.
All articles
19 articles by Derrick Smith, newest first.
Enterprise Positioning ·
The Cost of Identity Uncertainty: What Happens After MFA
Strong authentication was money well spent. It changed nothing about what happens after the door opens.
SOC Operations ·
12 Questions to Ask Before Evaluating Session Monitoring
Many products say continuous. These questions find out what that actually means.
Threat Analysis ·
When a Valid Session Changes Hands: The Evidence Behind Each Takeover
The Operator Problem named six ways the binding breaks. Here is what evidence can catch each one.
Privacy by Architecture ·
Content-Blind Behavioral Telemetry: Security Signals Without Reading the Work
Security needs visibility. Employees deserve privacy. The architecture can serve both.
Enterprise Positioning ·
Privileged Sessions: Where Losing Operator Continuity Costs the Most
Not every session carries the same risk. Start where a takeover is a company ending event.
Category Strategy ·
Continuous Authentication vs. Session Monitoring vs. Continuous Identity Confidence
Related terms, different questions. Sorting the vocabulary the market keeps blending.
SOC Operations ·
Continuous Authentication Without Constant Lockouts: The Proportionate Response Model
The hardest problem in behavioral security is not detection. It is deciding what to do next.
Enterprise Positioning ·
IAM vs. ITDR vs. EDR vs. UEBA: Where Operator Continuity Fits
Different layers answer different questions. Here is the one that still needs an owner.
Category Strategy ·
NIST SP 800-63B-4 and the Future of Session Monitoring
Identity guidance now extends past the login event. Here is what the standard actually says.
Post-Login Security ·
Authentication Ends. Trust Shouldn't.
Why post-login security is becoming cybersecurity's biggest blind spot.
Session Security ·
The Operator Problem
The session is legitimate. The operator may not be.
AI Threats ·
AI Agents Need Identity Too
Why continuous identity confidence applies to humans and AI agents.
SOC Operations ·
From Alert Fatigue to Behavioral Signal
Why behavioral anomalies beat environmental metadata.
Session Security ·
The Token Duration Tradeoff
How continuous verification resolves security vs. productivity.
Enterprise Positioning ·
Completing Zero Trust with Continuous Identity Confidence
The missing signal inside every policy decision.
AI Security ·
AI Agents and the New Attack Surface
Why prompt injection is structural, and what defense requires.
Threat Analysis ·
Session Hijacking in 2026: The Attack That Bypasses MFA
Why stolen tokens are more effective than stolen passwords.
Threat Landscape ·
How Modern Attackers Operate Inside Trusted Sessions
Stolen credentials, session tokens, and the post-authentication kill chain.
Category Strategy ·
The Security Gap After Authentication
Why IAM and MFA Leave Sessions Unprotected.